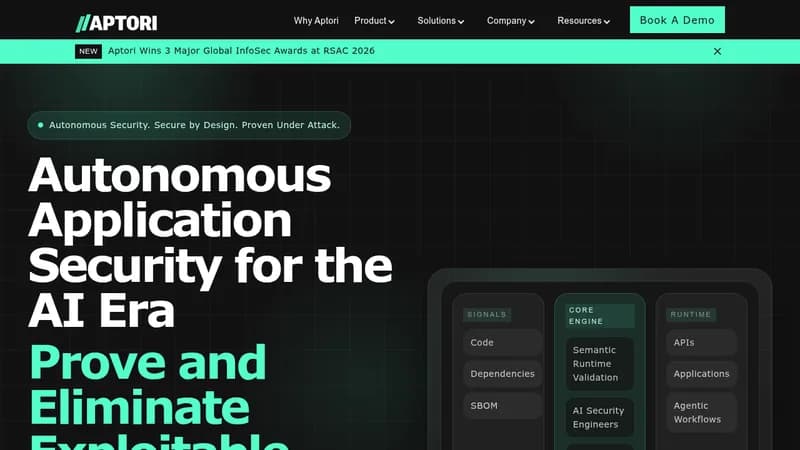
Aptori is an autonomous application security platform that continuously validates and proves exploitability of vulnerabilities across code, APIs, dependencies, and runtime. It combines code analysis, software composition intelligence, semantic runtime validation, and autonomous adversarial testing to uncover real vulnerabilities, prove exploit paths, and drive deterministic remediation. The platform uses AI security engineers that act as autonomous agents to perform continuous offensive security testing, correlate exploit paths across signals, and generate developer-ready fixes. Aptori covers application security testing, API security testing, software composition analysis (SCA), secure code review (modern SAST), and AI detection & response (AIDR). It is designed for complex, API-driven enterprise environments and supports CI/CD and production deployments, including private deployment with full data control.
Key Features
- Semantic Runtime Validation: Continuously tests real application behavior across APIs, identities, workflows, and data paths to prove exploitability.
- AI Security Engineers: Autonomous agents that perform adversarial testing, correlate exploit paths, and generate precise fixes.
- Unified Security Coverage: Combines code, dependency, SBOM, and runtime evidence into a single model of exploitable risk.
- Deterministic Remediation: Provides developer-ready fixes with validated exploit evidence.
- On-prem and Private Deployment: Supports air-gapped and private deployment options.
Use Cases
- Application Security Testing: Identify and validate real vulnerabilities across code, APIs, and runtime.
- Attack Surface Monitoring: Continuously discover exposed endpoints, shadow APIs, drift, and emerging attack paths.
- Multi-Tenant & Business Logic Testing: Uncover IDOR, BOLA, authorization gaps, and workflow abuse.
- Pen Testing: Automate offensive testing at scale and continuously validate what attackers can actually exploit.
Who It’s For
- Enterprise security teams
- Engineering teams
- Telecom and critical infrastructure organizations
- Organizations securing AI-driven and agentic applications
Key Benefits
- Proves real-world exploitability, not theoretical risk
- Reduces noise by eliminating false positives
- Accelerates remediation without slowing release velocity
- Supports private deployment with full data control