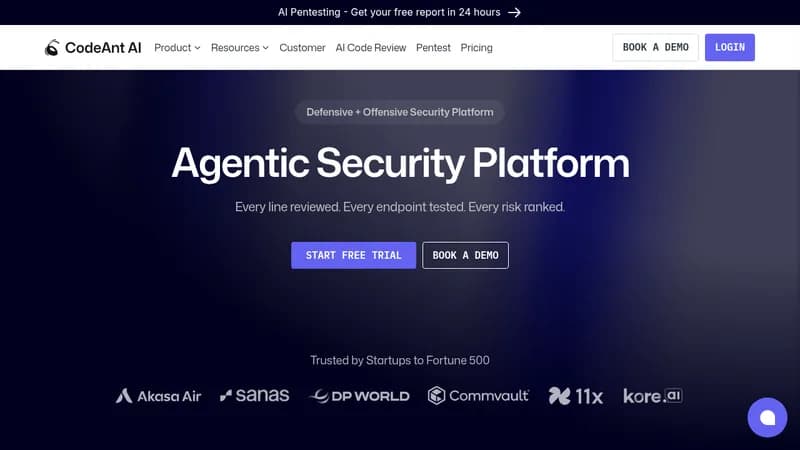
CodeAnt AI is an agentic security platform that combines defensive and offensive security capabilities in one AI-native solution. It helps developers and security teams catch vulnerabilities early in the development lifecycle and perform AI-driven penetration testing on deployed applications.
Key Features
- CLI & IDE Integration: Security checks run at the first keystroke, before code is committed. Supports VS Code, Cursor, JetBrains, and CLI.
- AI Code Review: Provides inline reviews, sequence diagrams, and AI learnings on every pull request with full codebase context, reducing review time by 80%.
- AI SAST: Unified static analysis covering code (SAST), infrastructure-as-code (IaC), dependencies (SCA), secrets, and SBOM generation.
- Offensive Pentesting: Maps public exposure (subdomains, IPs, JS bundles, leaked secrets) and runs 500+ exploit agents in chained attacks (SQLi, XSS, SSRF, BOLA, IDOR, auth bypass). Includes grey box testing using intelligence from the codebase.
- Compliance: Supports SOC 2 Type II, HIPAA, GDPR, and PCI DSS with audit-ready reports.
Pricing
- Defensive: 14-day free trial, no credit card required.
- Offensive: Free penetration test; pay only on high and critical findings. Low and medium findings are always free.
Who It’s For
Trusted by startups to Fortune 500 companies, CodeAnt AI is designed for CISOs, security leaders, engineering managers, and developers looking to embed security into their development workflow and validate it with continuous AI-powered pentesting.
Key Benefits
- Catches issues before a single line is committed
- Reduces code review time by 80%
- Unified SAST covering code, infrastructure, and dependencies
- AI penetration test with 500+ exploit agents and chained attacks