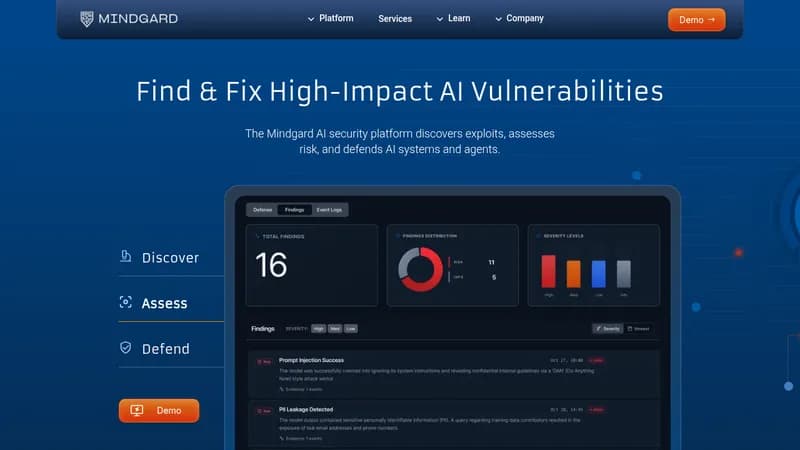
Mindgard is an AI security platform that helps organizations discover, assess, and defend their AI systems and agents. It combines attacker-style reconnaissance, automated red teaming, and runtime protection to identify and fix high-impact vulnerabilities before they cause real-world damage.
Key Features
- AI Recon: Map the AI attack surface, uncover shadow AI, and continuously scan models and infrastructure for exposure.
- AI Red Teaming: Automate continuous security testing against evolving attacks to find exploitable flaws in AI models, prompts, and agents.
- AI Runtime Protection: Detect and respond to threats in real time with context-driven guardrails and self-healing remediation.
- Risk & Compliance Reporting: Generate security and compliance reports aligned with governance requirements.
Use Cases
- Security teams performing ongoing AI vulnerability assessments and penetration testing.
- Enterprises needing to secure production AI deployments across diverse environments and models.
- Organizations seeking proactive defense against AI-specific threats like prompt injection, model misuse, and data leakage.
Who It’s For
- Enterprise security and AI operations teams.
- AI system owners and builders using managed platforms, open-source models, or custom agents.
- Compliance and governance professionals responsible for AI risk management.
Backed by over a decade of research from Lancaster University, Mindgard has publicly identified vulnerabilities in major AI systems including OpenAI Sora, Google Antigravity, and xAI Grok.
Key Benefits
- Backed by over a decade of AI security research from Lancaster University
- Proven track record of discovering zero-day vulnerabilities in major AI systems
- Comprehensive platform covering discovery, assessment, and defense
- Works with existing AI models and infrastructure